

Business Innovation
THAITEX focuses on the development and promotion of corporate innovation to adjust and develop its business to be able to grow stably and sustainably, as well as to create value in the long term for the business and create value or benefit to customers or related parties. Therefore, the organization’s innovation development and promotion policy has been formulated as follows:
Information Technology & Cybersecurity
IT Security and Cybersecurity Management
Objectives and Scope
Thai Rubber Latex Group Public Company Limited has established an Information Technology Security Policy to serve as a framework for managing information security and to ensure confidence in the organization’s IT systems.
- Establish information security standards for systems and networks
- Align with international standards such as ISO/IEC 27001 and ensure continuous improvement
- Communicate the policy to all employees and ensure strict compliance
- Define guidelines for executives, system administrators, employees, and external parties.
- Conduct regular review and evaluation on an annual basis
Policy Framework
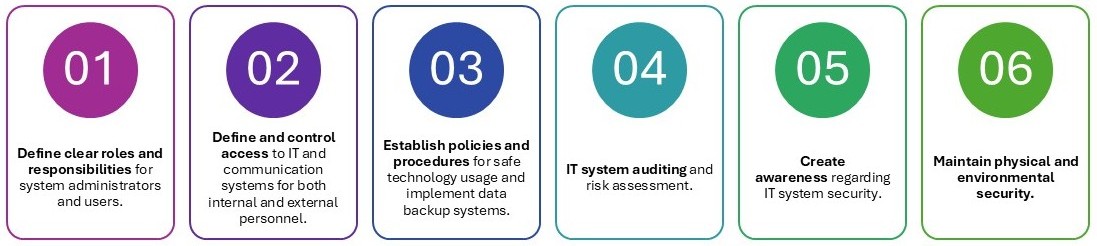
Information Security Incident Response
The Company defines Standards, Guidelines, and Procedures to systematically manage information security. These measures aim to mitigate risks, prevent potential impacts on business operations, personnel, and assets, and ensure business continuity in a secure environment. ร
Cybersecurity Activities
- Report emerging threats to the Board of Directors and Management on a monthly basis.
- Promote cybersecurity awareness through various communication channels
- Conduct cybersecurity attack simulations at least once per year
- Organize seminars and engagement activities to enhance awareness
- Publish Security Tips and Security Alerts
- Conduct Phishing Drills to strengthen employees’ awareness and response capability
Cybersecurity Awareness
The Company is committed to fostering a strong cybersecurity culture by enhancing employee awareness and ensuring effective response to cyber threats.
Annual Cybersecurity Activities and Incident Report 2025
Operational Initiatives
- Quarterly Threat Statistics Reporting: Providing comprehensive reports on external cyber threat statistics to the Board of Directors and Department Managers every quarter.
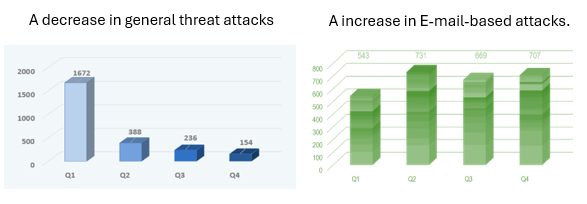
- Security Awareness Campaigns: Developing and disseminating educational content through various corporate channels to provide knowledge on cyber threats and preventive measures. Monthly security bulletins are sent via e-mail to all executives and employees.
- Cyber Attack Simulations: Conducting simulations of cyber threats to test employee knowledge and understanding regarding suspicious e-mail handling.
- Annual Cybersecurity Awareness Training: Mandating cybersecurity training for all executives and employees on an annual basis.
- Continuous Professional Development: Regularly sending the Cybersecurity Team to attend advanced training and seminars to stay updated with evolving technologies.
Technology Risk Management: The Company conducts an annual cyber risk assessment to continuously improve and elevate our cybersecurity posture.
- Identification & Mitigation: Identifying, monitoring, and assessing risk factors while implementing mitigation activities to proactively address emerging cyber threats.
- System Protection (Protect): Enhancing access control processes for critical systems and deploying modern hardware/software solutions tailored to current work environments. These measures aim to increase security and reduce data theft risks in compliance with the computer-Related Crime Act and Personal Data Protection Act (PDPA).
- Detection & Governance (Detect): Evaluating the efficacy of security technologies and critical system access. The Company has updated its data confidentiality classification policies and implemented anomaly detection systems to enhance cybersecurity surveillance.
- Incident Response (Respond): Maintaining continuous readiness for abnormal situations through drills and simulations of critical IT system attacks, such as Ransomware and data breaches. This includes regular Phishing Simulation Tests to evaluate employee response to deceptive e-mails.
- System Recovery (Recover): Conducting annual Backup & Recovery tests to ensure system restorability. All tests in 2025 successfully met the recovery time and point objectives.